

Network architecture
Promptless runs on AWS, inside its own virtual private cloud (VPC). Use this page to answer the infrastructure questions in a security assessment. It shows how events and users reach Promptless, how Promptless keeps each customer organization’s data separate, and which controls protect that data.
Use cases
Section titled “Use cases”- Give a security reviewer a diagram of how data flows between your tools, Promptless, and its subprocessors.
- Answer questions about how Promptless isolates your organization’s data from other customers’ data.
- Confirm the encryption and access controls that protect data in the Promptless cloud.
Infrastructure overview
Section titled “Infrastructure overview”The diagram shows the path from the events and people that start work in Promptless to the systems Promptless stores data in and publishes to:
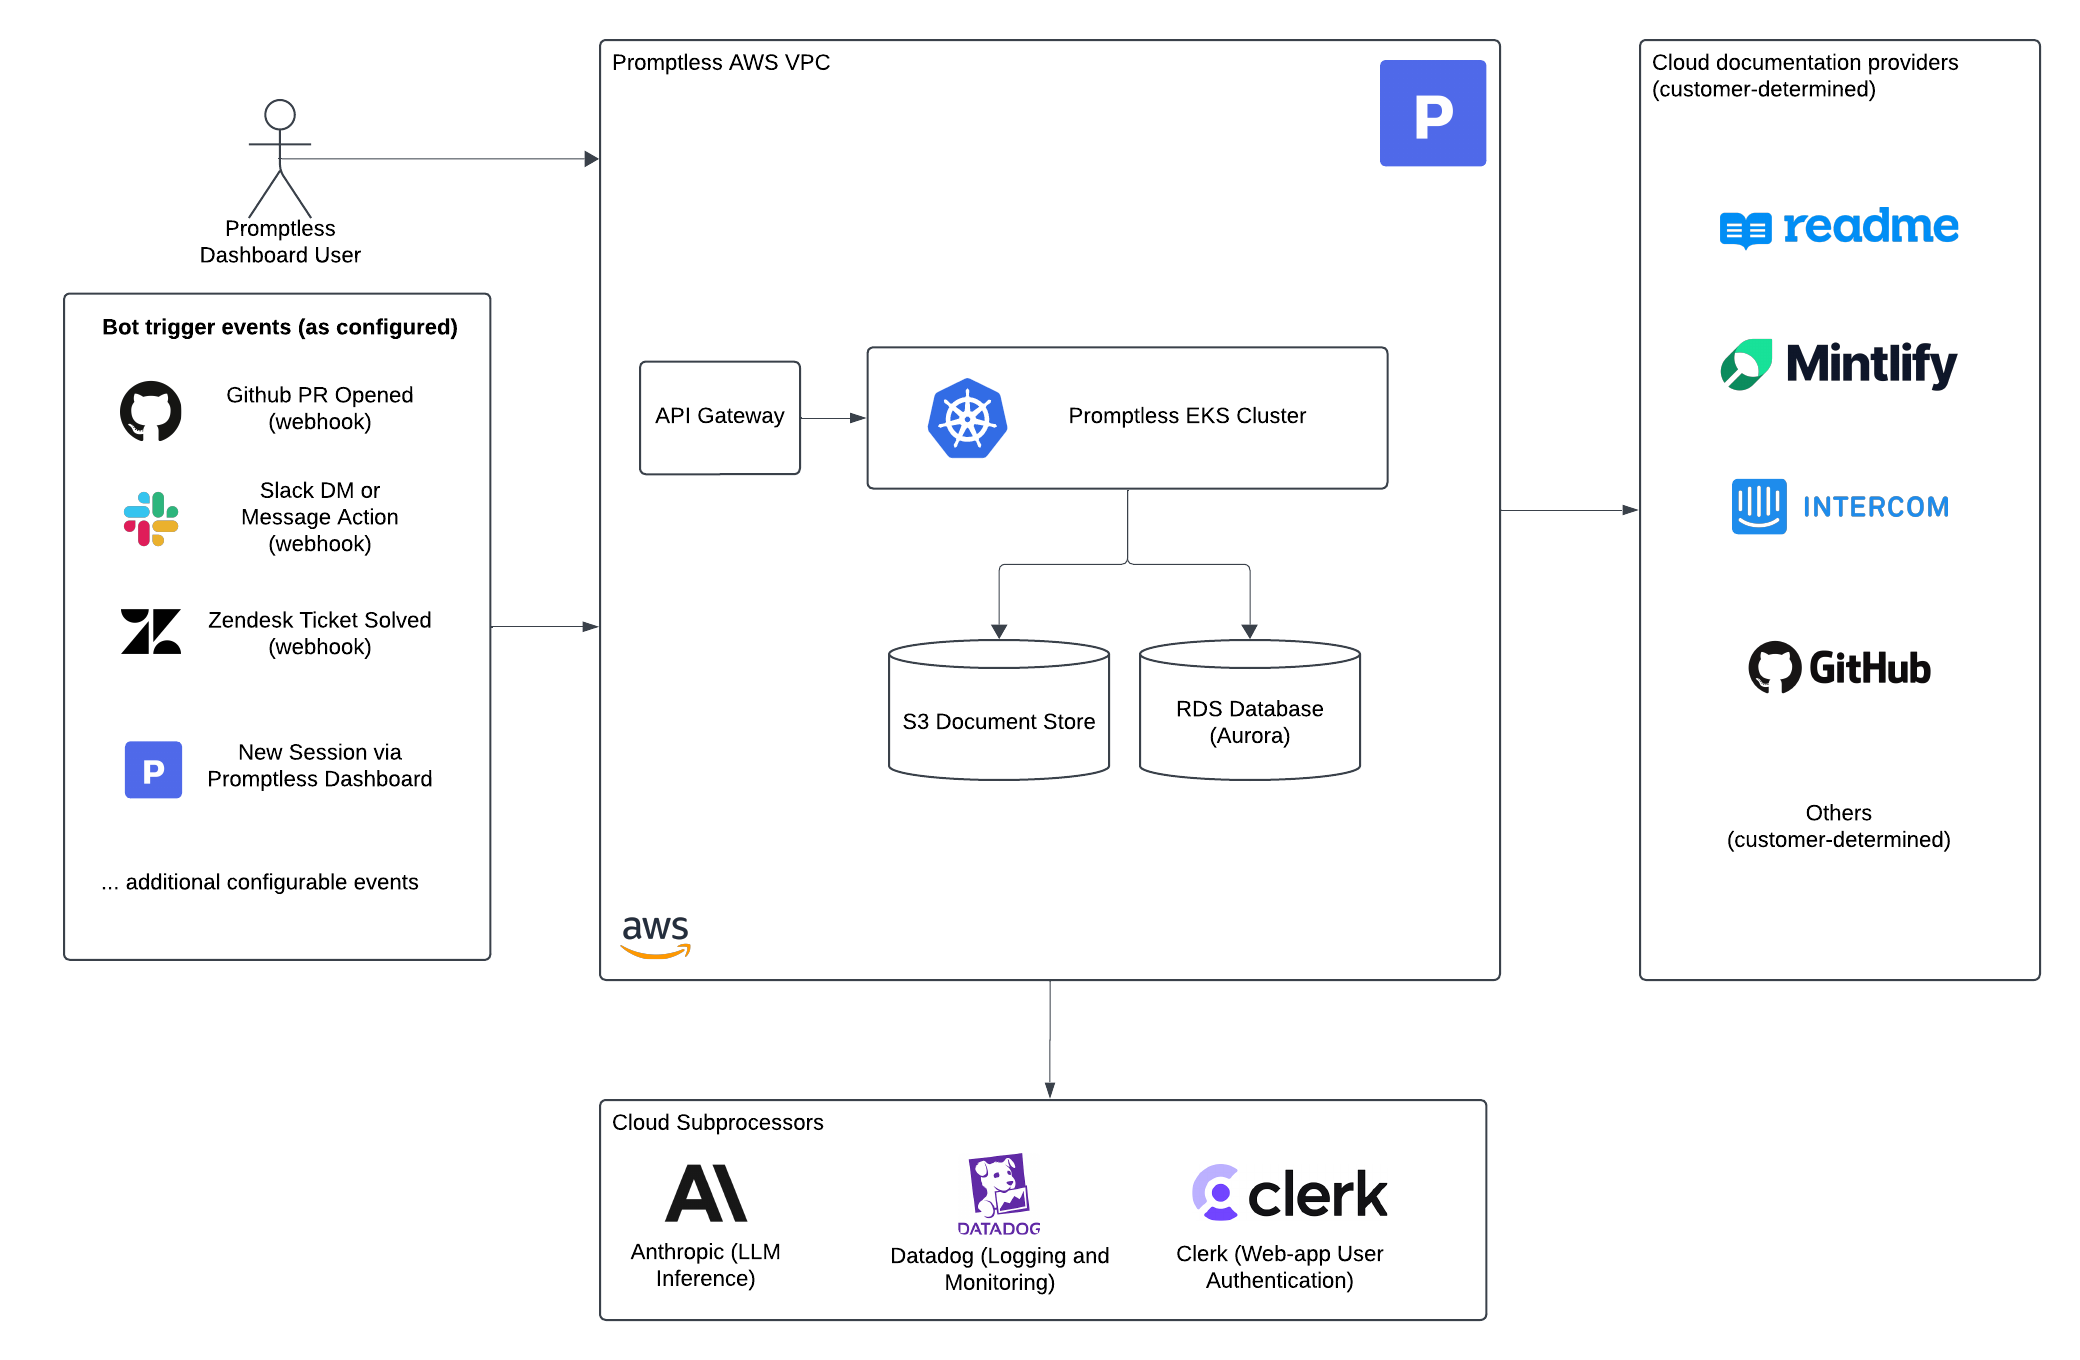
- Dashboard users and configured trigger events reach the Promptless AWS VPC. Trigger events include a GitHub pull request webhook, a Slack message action, or a Zendesk ticket webhook.
- Inside the VPC, an API gateway passes requests to the Promptless EKS cluster.
- The cluster stores data in an S3 document store and an RDS (Aurora) database.
- The cluster publishes documentation to the providers you choose, such as ReadMe, Mintlify, Intercom, or GitHub.
- The cluster calls cloud subprocessors for language model inference, logging and monitoring, and web app user authentication. For the current list, see subprocessors.
The infrastructure is designed for security at every layer, high availability and fault tolerance, scalability, and monitoring and observability.
Multi-tenant security model
Section titled “Multi-tenant security model”Promptless keeps customer organizations apart through logical separation:
- Every piece of data, such as users, suggestions, and trigger events, carries an organization ID.
- Every database query is scoped to the requesting organization.
- Authorization checks prevent access to another organization’s data.
- Customer organizations share no data context.
Shared infrastructure reduces the number of infrastructure assets to track and maintain, and the number of data access points across the system.
Key security measures
Section titled “Key security measures”These are the main measures that protect data in Promptless:
| Measure | How Promptless applies it |
|---|---|
| Encryption in transit | All data in transit is encrypted with TLS 1.2 or later. |
| Encryption at rest | Data stored in the Promptless database is encrypted with AES-256. |
| Access controls | A combination of access controls, including role-based access control (RBAC), limits sensitive data to authorized users. |
| Principle of least privilege | Each user gets only the permissions their role needs. |
| Logical separation of data | All data is tagged with customer identifiers, which gives multiple layers of logical separation between customers. |
For more detail about the network architecture, or to discuss specific security requirements, email the security team at security@gopromptless.ai.